Firewall Indicator
Your security posture, one glance from the status bar.
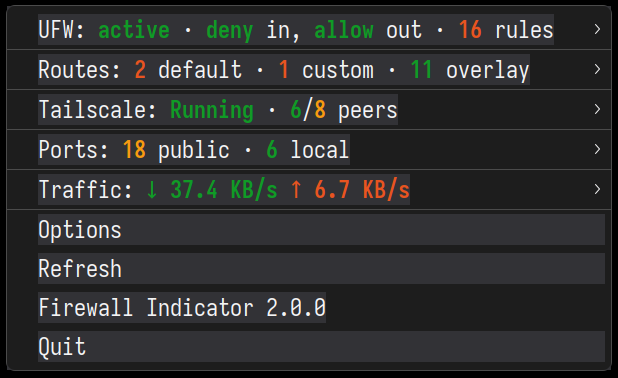
Panel status for a Linux desktop. Firewall Indicator summarizes UFW, custom routes, Tailscale or Headscale, fail2ban, listening ports, and upload/download traffic — in the GNOME top bar, a Waybar module or any system tray.
- Platform
- Linux desktop
- Built with
- Rust
What it does
Firewall at a glance
UFW when it is installed, otherwise nftables or firewalld — active state, default policy and rule count, with a rootless fallback to config files.
Routes and overlays
Default, custom and overlay routes kept apart; Tailscale, Headscale and WireGuard peers, addresses and exit nodes reported live.
Exposure and intrusion
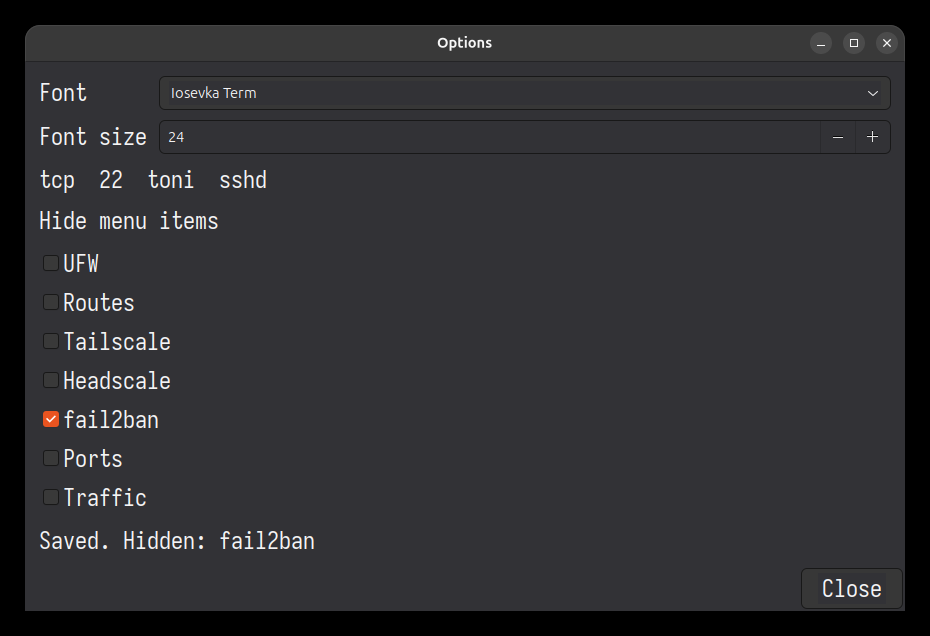
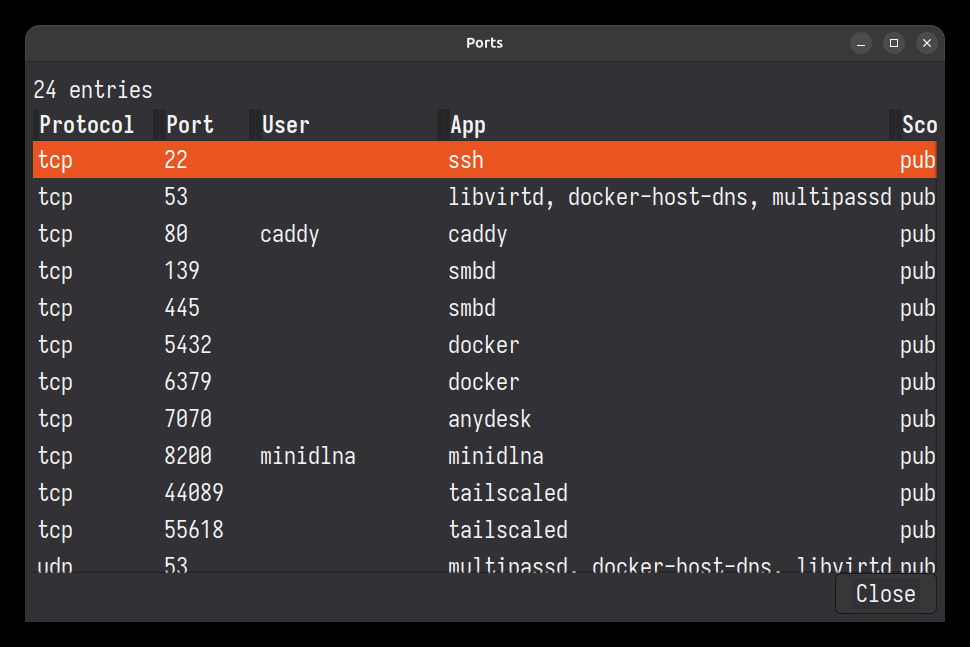
fail2ban service state with per-jail banned counts, plus listening TCP sockets and UDP services.
Traffic
Download and upload rate and bytes since boot on the interfaces that carry the default route.
One binary, every desktop
Written in Rust with no Python dependency: a GNOME Shell extension, a Waybar module for Hyprland and Omarchy, and a StatusNotifier tray for KDE and Xfce.
Screenshots